Passkeys, FIDO2 & WebAuthn for .NET

Enabling simple, secure authentication and mfa using FIDO2 / WebAuthn

Scenario: Passkey sign-in with a username

A username-first passkey flow: no password anywhere, but the Relying Party still asks for a username up front rather than letting the authenticator surface a discoverable credential on its own (see the usernameless scenario for that). User verification (PIN/biometrics) is optional here, set via UserVerification.

Note: "passwordless" means no password is sent over the internet or stored in a database. A PIN or biometric might still be used locally, by the authenticator, to unlock the passkey.
Register user

Sign in

Explanation: Passkey sign-in with FIDO2

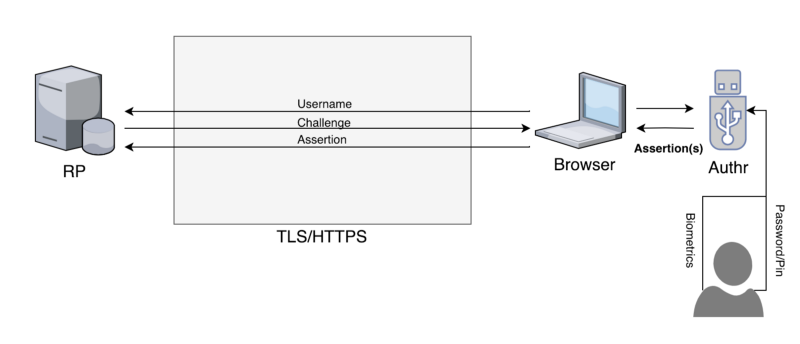
In this scenario the passkey is looked up by username, rather than being discoverable on its own. The flow is visualized in the figure below.

figure visualizing username and challenge sent together with assertion

Setting UserVerification to required has the authenticator confirm the person via PIN or biometrics as part of unlocking the passkey — possession of the private key and verification of the person, in one gesture. Setting it to discouraged instead checks only user presence, minimizing the interaction needed to sign in.

Read the source code for this demo here: passwordless.register.js and passwordless.login.js — these set the options that make this scenario what it is. The ceremony they run is shared by every scenario and lives in webauthn.js.